


Judge twice, buy once: GuideTorrent offers free demo downloads for the Fortinet NSE 4 - FortiOS 7.0 material so you can tell if it suits you — 175 practice questions for the NSE4_FGT-7.0 exam behind the door.
Fortinet NSE4_FGT-7.0 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Security Profiles | - Antivirus, IPS, and application control - Web filtering and DNS filtering |
| Firewall Policies and Authentication | - User authentication and identity-based policies - Firewall policy creation and traffic flow control |
| High Availability and Performance | - HA cluster configuration and synchronization - Performance monitoring and optimization |
| Network Security Architecture and FortiGate Deployment | - Basic network interface and routing configuration - FortiGate system configuration and initial setup |
| VPN Technologies | - SSL VPN setup and client access - IPsec VPN configuration and troubleshooting |
| Logging, Monitoring, and Troubleshooting | - Traffic logs and event analysis - Diagnostic tools and troubleshooting workflow |
Fortinet NSE4_FGT-7.0 Exam: Questions Candidates Ask
Basic networking knowledge recommended; no mandatory prerequisites, but FortiGate fundamentals experience is advised. Vendors revise eligibility rules periodically, so confirm the current requirements on the official page (official NSE4_FGT-7.0 exam page) before registering.
Delivery is instant — an automatic email within a minute of payment, unlimited devices, and 7*24 online service (replies within two hours) if anything's missing after 2 hours; check spam first. If you fail the corresponding NSE4_FGT-7.0 exam within 60 days of purchase, we refund all the cost you paid: send a scanned enrollment slip plus the official Score Report PDF within 2 days of the exam, processed within 7 days. Excluded: exams within 3 days of purchase, candidate names that don't match the payer, and free or expired products. Alternatively, exchange for two equal-value products free.
105 minutes for Approximately 60 questions. Train the pace in advance: timed practice sessions turn the exam clock from a threat into a habit.
Yes:
Official courses build the base; the 175 practice questions for the Fortinet NSE 4 - FortiOS 7.0 — every answer expert-verified — build the readiness.
The Fortinet NSE 4 - FortiOS 7.0 blueprint spans 6 domains — including Security Profiles, High Availability and Performance, Network Security Architecture and FortiGate Deployment. Study in proportion to the weightings; the complete outline above details every subtopic.
Yes — free demo downloads let you tell whether the Fortinet NSE 4 - FortiOS 7.0 material suits you before purchasing. Purchases include 365 days of free updates, each new version emailed immediately; renew afterward at 50% off.
Through the vendor's official registration channels:
The Fortinet NSE 4 - FortiOS 7.0 is delivered Online proctored or authorized test center — choose the arrangement that fits you when booking.
The Fortinet NSE 4 - FortiOS 7.0 is Fortinet's certification exam for Fortinet Certified Professional (FCP) Network Security / NSE 4, at the Professional level. These certifications are valued precisely because they're demanding — passing one validates real capability. Related credentials include Fortinet Certified Associate (FCA), Fortinet Certified Professional (FCP) Network Security, Fortinet NSE 5, Fortinet NSE 6.
Fortinet NSE 4 - FortiOS 7.0 Sample Questions:
An administrator is configuring an IPsec VPN between site A and site B.
The Remote Gateway setting in both sites has been configured as Static IP Address.
For site A, the local quick mode selector is 192.168.1.0/24 and the remote quick mode selector is 192.168.2.0/24.
Which subnet must the administrator configure for the local quick mode selector for site B?
- A. 192.168.1.0/24
- B. 192.168.2.0/24
- C. 192.168.0.0/24
- D. 192.168.3.0/24
Correct Answer: B 🗳️
Which of the following are valid actions for FortiGuard category based filter in a web filter profile ui proxy-based inspection mode? (Choose two.)
- A. Learn
- B. Exempt
- C. Allow
- D. Warning
Correct Answer: C,D 🗳️
Examine this FortiGate configuration: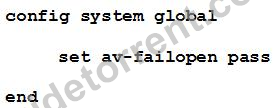
Examine the output of the following debug command:
Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that require inspection?
- A. It is allowed, but with no inspection
- B. It is allowed and inspected, as long as the only inspection required is antivirus.
- C. It is allowed and inspected as long as the inspection is flow based
- D. It is dropped.
Correct Answer: D 🗳️
Refer to the exhibit.
In the network shown in the exhibit, the web client cannot connect to the HTTP web server. The administrator runs the FortiGate built-in sniffer and gets the output as shown in the exhibit.
What should the administrator do next to troubleshoot the problem?
- A. Execute a debug flow.
- B. Execute another sniffer in the FortiGate, this time with the filter "host 10.0.1.10"
- C. Run a sniffer on the web server.
- D. Capture the traffic using an external sniffer connected to port1.
Correct Answer: A 🗳️
Which two types of traffic are managed only by the management VDOM? (Choose two.)
- A. DNS
- B. Traffic shaping
- C. FortiGuard web filter queries
- D. PKI
Correct Answer: A,C 🗳️
Viewing page 1 out of 35 pages.
Viewing questions 1-5 out of 175 questions.


